Between your systems and the threat.

The managed service between your infrastructure and cyber threats. Detection, incident response and threat intelligence, operated 24/7.

A new approach to the SOC

Cybersecurity should not be reserved for large organisations.

Rempart is the managed SOC of SecuLabs' CSIRT practice. A sovereign platform that collects your logs, detects malicious activity and mobilises our experts 24/7, without relying on any third party.

24/7
Continuous monitoring by human analysts
~30
Days from order to first triage in production
0
External cloud: everything is operated by SecuLabs in Switzerland
10+
CSIRT experts available for a critical incident

From data to visibility

  1. Multi-source collectionEndpoint logs by agent, network logs by Syslog, cloud and Microsoft 365 logs by API.
  2. Centralised storageEvents are normalised, retained and available for search and investigation.
  3. Clear visualisationDashboards and searches make your systems' activity readable, before detection even starts.

The lifecycle of an event

From the arrival of the raw log to the incident notification, every step is instrumented to guarantee traceability and response time.

  1. Collection

    Your logs are brought in through the agent, Syslog or API, then normalised into a common schema before feeding your Security Data Lake.

  2. Detection

    The detection engine queries the logs continuously and applies SecuLabs rules aligned with the MITRE ATT&CK framework.

  3. AI triage

    Triage by LLM & RAG reduces false positives and brings back the context of your information system in detail, for a precise analysis.

  4. Investigation

    Our analysts handle P1 and P2 alerts, qualify the malicious activity and notify you as soon as an incident is confirmed.

Included in Rempart Detect

Beyond logs, Detect watches your cloud services and each host's exposure to known vulnerabilities, with no extra agent or connector.

Vulnerability management, per host

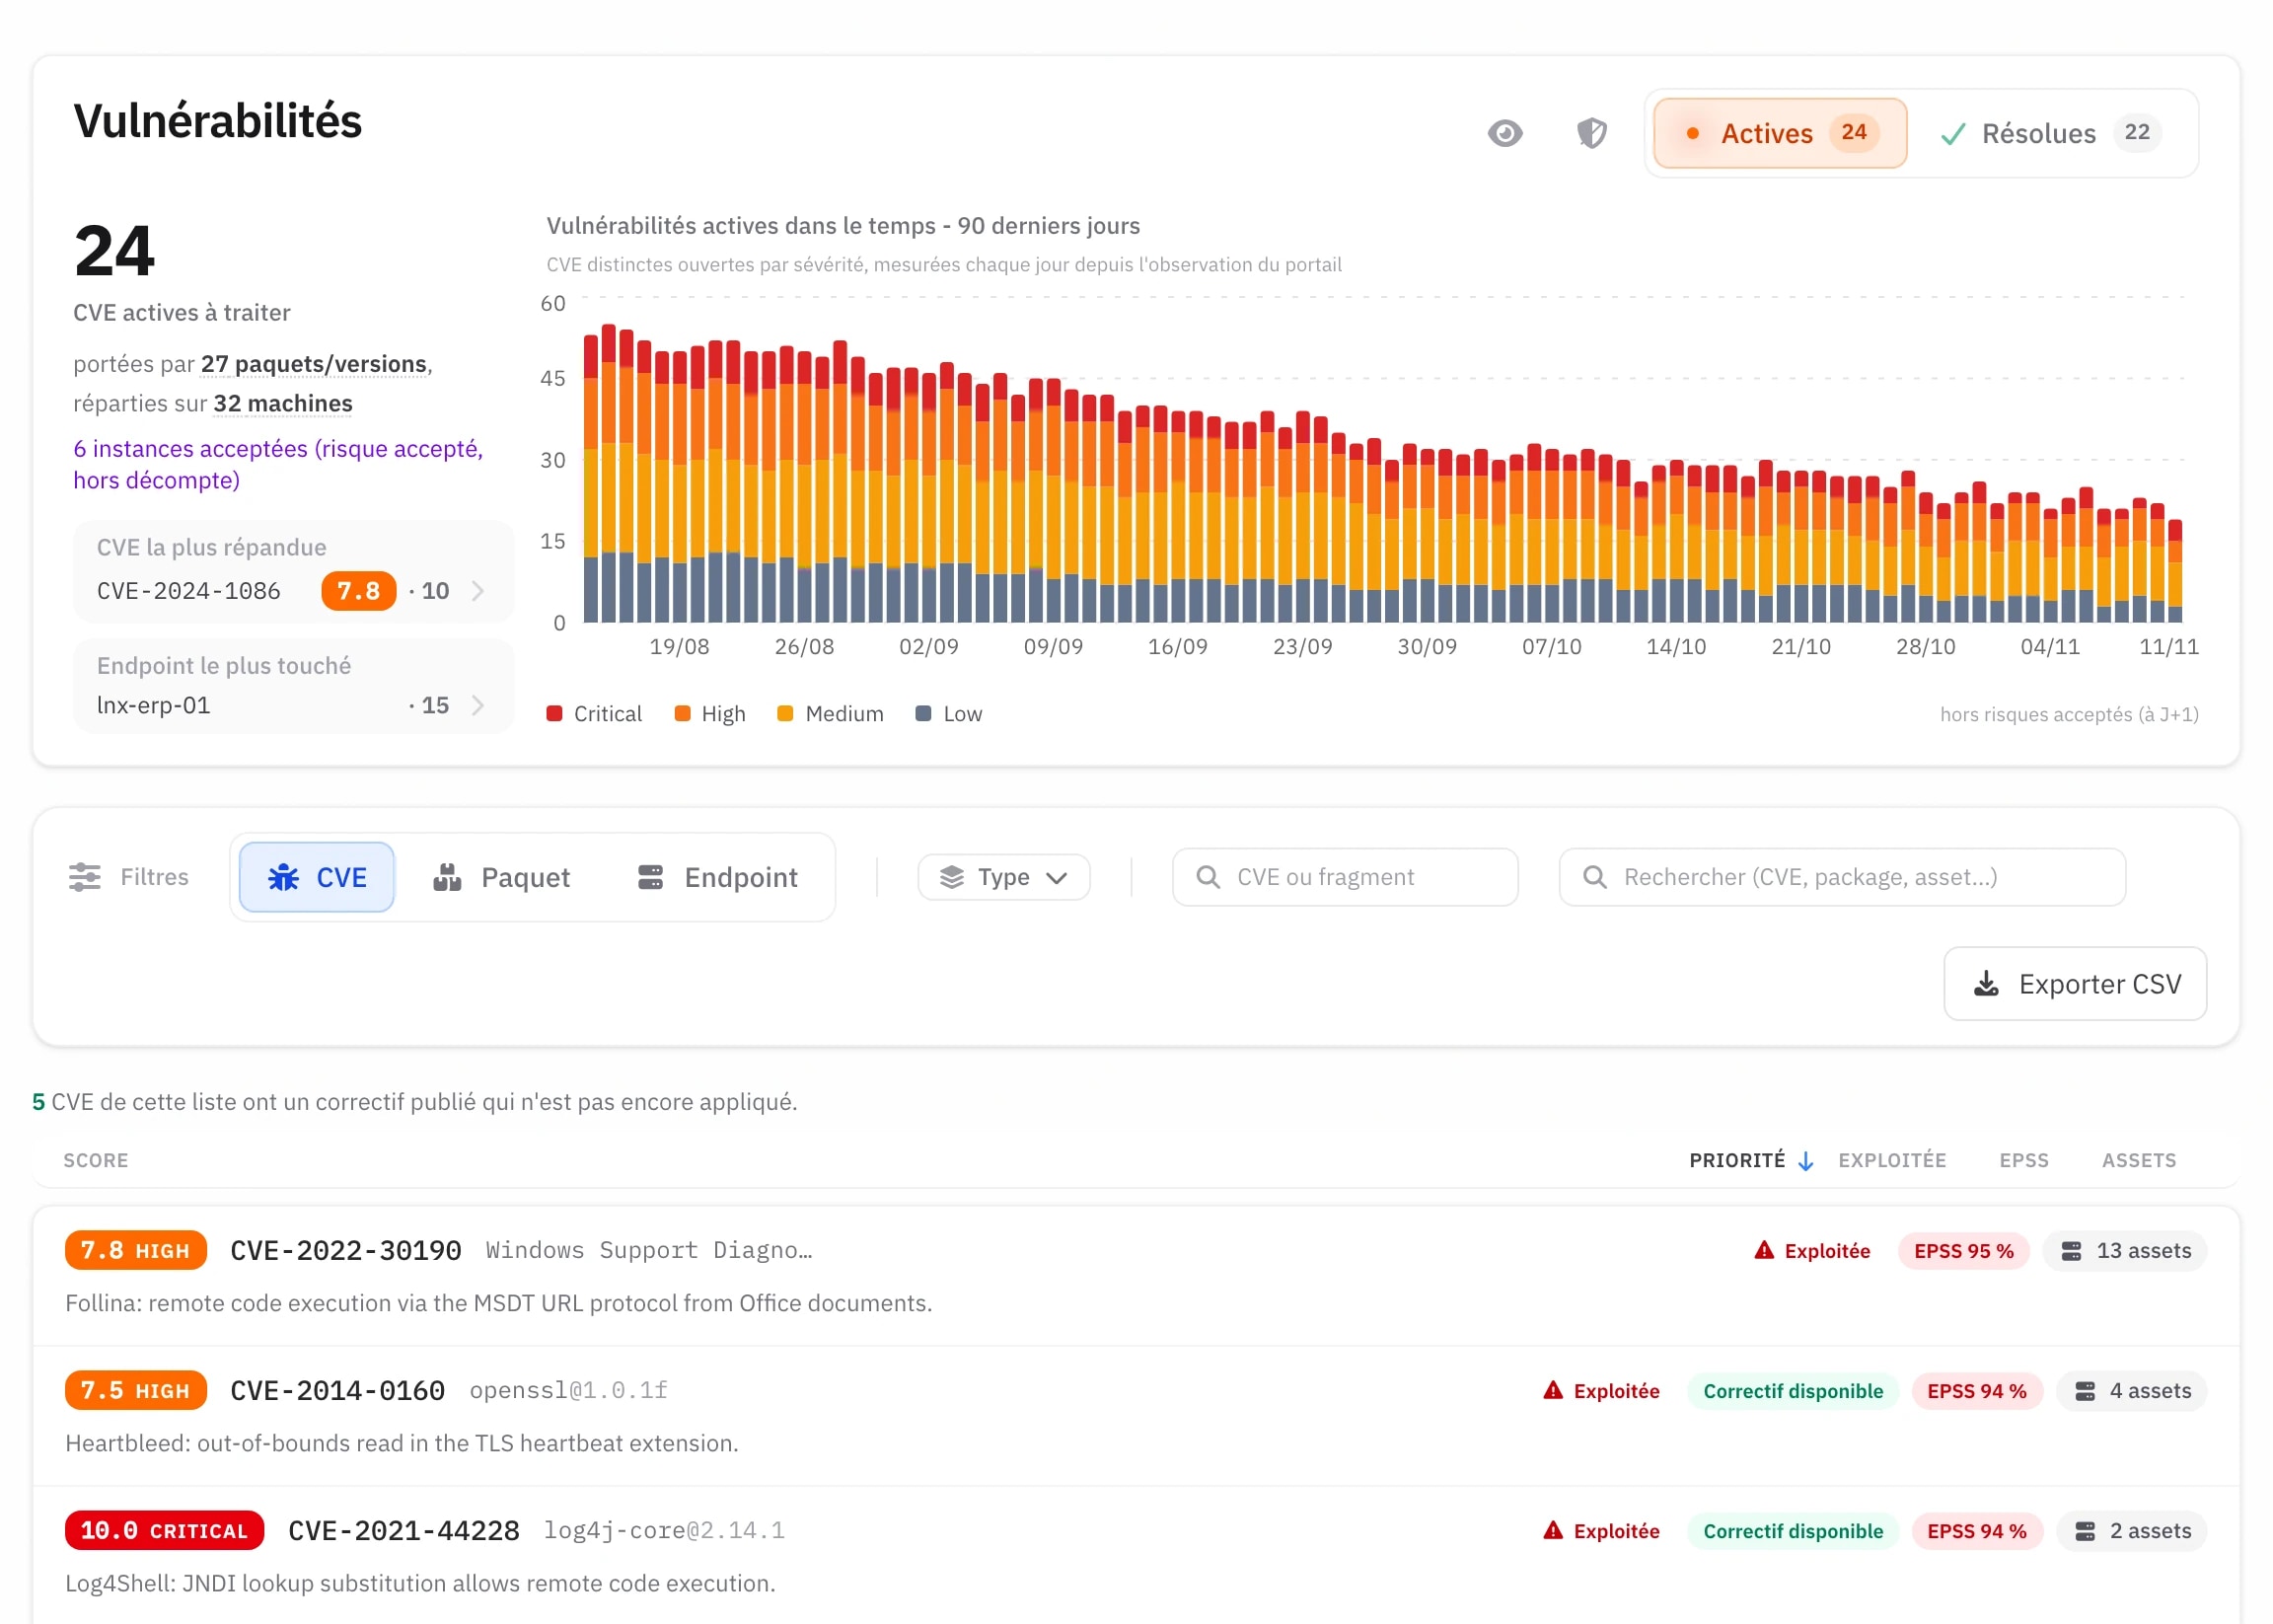
The agent already deployed for collection also inventories the software installed on each host and checks it continuously against known vulnerabilities (CVE): an always up-to-date view, prioritised by severity, with no extra agent.
portail.rempart.ch/vulnerabilitiesDemonstration data
Vulnerabilities view of the Rempart portal, on demonstration data: 24 active CVEs on 32 machines, their trend by severity over 90 days, then the prioritised list with known exploitation, EPSS score and available fix.

Microsoft 365 and your cloud services

For cloud services, collection relies on the providers' secure APIs, with no intermediate connector to deploy or maintain. Microsoft 365 is the textbook case: its mail, identities, third-party applications and tenant administration are all monitored.

Your Microsoft 365 tenant

  • ExchangeMail

  • SharePointTeamsFiles and Teams

  • Entra IDIdentities

  • Third-party applications

  • MicrosoftTenant administration

  • Microsoft DefenderDefender alerts

Your other cloud services

  • Your existing EDR

  • DMS & other SaaS

Plug & play deployment

Operational in 30 days, without reinventing your stack.

Four steps paced by our teams. You have no tooling to buy and no project to run.

  1. Scoping & delivery

    Roles and points of contact defined, deployment of the solution begins.

  2. Connecting the sources

    Agents on your endpoints, Syslog & APIs for your specific equipment. Collection starts. First logs ingested within 48 hours.

  3. Qualification & tuning

    Our analysts calibrate the rules to your context.

  4. Switch to 24/7 production

    The SOC moves to active monitoring. You receive your portal access.

Days of expertise are included in the offer, to use at your own pace: equipment configuration, cyber advice, we are at your service.

A closed circuit, operated in Switzerland.

We chose to build and run Rempart's infrastructure ourselves rather than rent capacity from a hyperscaler. No data you entrust to us leaves this perimeter, and a single provider is accountable to you for it.

Your systems

  • Hosted in Switzerland

    Tier 3 datacenter in Geneva, on our own hardware, with no outside third party.

  • Flexible retention

    A retention period aligned with your regulatory requirements and your needs.

  • AI run locally

    Open-source models run on our own GPUs, locally, with no external cloud.

Hugo Bourget

A Swiss SME does not necessarily have the human resources of a large group. Rempart gives it the visibility of a structured SOC, with the team it actually has.

Hugo BourgetTechnical Lead

Ready to see Rempart in action?

Let's discuss your specific needs and build a solution suited to your context together.