Compliance under control.
Resilience strengthened.
Cyber strategy, regulatory compliance, risk management, business continuity and an outsourced CISO: we structure your security posture so that it becomes a driver of trust and competitiveness.
Governance, risk, compliance: the framework for cybersecurity under control.
GRC is an integrated approach that aligns your security strategy with your business objectives. It combines clear governance, proactive risk management and compliance with regulatory requirements.
Without a structured GRC framework, security decisions stay reactive, fragmented and costly. With a GRC approach, every investment is targeted, measurable and defensible before your management.
At SecuLabs, we turn GRC from an obligation into a competitive advantage, suited to the reality of your sector in Switzerland.
Governance
Cyber strategy, policies, organisation and steering of information security.
Risk
Identification, analysis and treatment of risks. Prioritisation by business impact.
Compliance
Alignment with standards (ISO 27001, NIST) and regulations (FADP, GDPR, FINMA, DORA).
CISO as a Service
No CISO, or looking to strengthen your team? Our experts take on the role of chief information security officer, part-time or full-time, to steer your cyber governance day to day.
Explore CISO as a ServiceStrategic
Vision, security policy, alignment with management
Tactical
Security plans, project management, coordination
Operational
Implementation, day-to-day monitoring, reporting
- Strategic
- Vision, security policy, alignment with management
- Tactical
- Security plans, project management, coordination
- Operational
- Implementation, day-to-day monitoring, reporting
Far more than an obligation: an advantage for every organisation.
Does your organisation operate in a regulated sector?
If you work in finance, insurance, healthcare, energy or critical infrastructure, you are subject to strict requirements (FINMA, DORA, NIS2, FADP). A structured GRC framework lets you demonstrate your compliance to regulators, avoid sanctions and turn these constraints into processes that genuinely strengthen your security. Our experts know the specific expectations of each Swiss and European regulator.
Does your organisation handle sensitive data?
Patient data, financial information, intellectual property, your customers' personal data: protecting these assets is a legal obligation and a commitment to your stakeholders. GRC helps you map your processing activities, put the right protection measures in place (DLP, encryption, access control) and prove your due diligence in the event of an inspection or an incident.
Is your company growing or putting structures in place?
Rapid growth, fundraising, entry into new markets, a first ISO 27001 certification: these are all moments when structuring your cyber governance becomes essential. Our engagements are sized to your organisation and your budget. We lay GRC foundations that will grow with you, without over-engineering or documents that end up in a drawer.
Is your company exposed to significant cyber risks?
Ransomware, supply chain compromise, data leaks, business disruption: if your organisation depends on digital systems, it is exposed. GRC lets you move from a reactive posture to proactive risk management: threat identification, continuity plans, crisis exercises and continuous improvement. It is the difference between suffering an incident and being prepared for it.
Regulations
- FINMABanks and securities firmsCircular 2023/1
- FADPPersonal data, SwitzerlandFederal act
- GDPRPersonal data, European UnionEU regulation
- DORADigital resilience of the financial sectorEU regulation
- NIS2Essential and important entitiesEU directive
Standards and frameworks
- ISO 27001Security management systemISO standard, certifiable
- NIST CSFCyber risk managementNIST framework
- ISO 22301Business continuityISO standard, certifiable
- SOC 2Controls at service providersAICPA attestation
- TISAXAutomotive industryENX label
- PCI DSSPayment card dataPCI SSC standard
- SWIFT CSPSWIFT network usersSWIFT programme
End-to-end support, from strategy to operations.
Tailored services, matched to your maturity and your challenges.
Cyber strategy & ISMS
Development of your cybersecurity strategy and security policy, and implementation of an information security management system (ISMS) compliant with ISO 27001.
- Security policy
- ISMS
- Roadmap
Security & maturity audit
An external, independent assessment of your security posture, run against the framework of your choice: ISO 27001, NIST CSF, FADP, FINMA or your own internal framework. Maturity analysis, identification of gaps and prioritised recommendations to move forward.
- Audit report
- Maturity grid
- Remediation plan
Certification readiness
Gap analysis, action plan and support all the way to certification. ISO 27001, SOC 2, TISAX and other recognised standards.
- Gap analysis
- Action plan
- Audit support
Business continuity (BCM)
Putting your resilience into practice: business continuity plan, cyberattack response plan and crisis management exercises (tabletop, contingency plan).
- BIA & BCP
- Response plan
- Crisis exercises
DPO as a Service
Data protection officer missions: FADP/GDPR compliance, protection measures, data leak prevention (DLP), oversight and awareness.
- Record of processing activities
- DPIA / PIA
- DLP policy
Internal control & TPRM
Support for your internal control system, supplier assessment (TPRM), security due diligence and support for outsourcing activities.
- Control matrix
- Due diligence
- Outsourcing governance
Pragmatic, certified, integrated by design.
We build GRC into every project from the start and into every stage of your cyber journey. Each engagement can be adapted and tailored to your needs.
A rigorous framework, tailored execution.
Our methodology builds on recognised standards and adapts to the specifics of each client.
1
Scoping & diagnosis
Understanding your context, objectives and constraints
2
Analysis & assessment
Current state, gap analysis, identification of priorities
3
Recommendations & roadmap
Prioritised action plan, concrete deliverables, tracking KPIs
4
Ongoing support
Implementation follow-up, coaching, iterative adjustments
GRC by Design
SecuLabs builds governance, risk and compliance into your project from the outset, and at every stage.
Certified teams.
Our experts hold the industry's most recognised certifications.
- OSCE3, Offensive Security Certified Expert 3, OffSec
- OSEP, OffSec Experienced Penetration Tester, OffSec
- OSWE, OffSec Web Expert, OffSec
- OSED, OffSec Exploit Developer, OffSec
- OSCP+, Offensive Security Certified Professional+, OffSec
- OSCP, Offensive Security Certified Professional, OffSec
- CRTE, Certified Red Team Expert, Altered Security
- CRTL, Certified Red Team Lead (Red Team Ops II), Zero-Point Security
- HTB CPTS, Certified Penetration Testing Specialist, Hack The Box
- CRTO, Certified Red Team Operator, Zero-Point Security
- CRTP, Certified Red Team Professional, Altered Security
- CARTP, Certified Az Red Team Professional, Altered Security
- AzRTE, Azure Red Team Expert, HackTricks Training
- GWAPT, GIAC Web Application Penetration Tester, GIAC
- HTB CWES, Certified Web Exploitation Specialist (ex-CBBH), Hack The Box
- HTB COAE, Certified Offensive AI Expert, Hack The Box
- eCPPT, Certified Professional Penetration Tester, INE Security
- GSNA, GIAC Systems and Network Auditor, GIAC
- GMON, GIAC Continuous Monitoring, GIAC
- CCSE, Check Point Certified Security Expert, Check Point
- CCSA, Check Point Certified Security Administrator, Check Point
- CCNA, Cisco Certified Network Associate, Cisco
- NSE 4, Fortinet NSE 4, FortiOS, Fortinet
- CSNA, Certified Stormshield Network Administrator, Stormshield
- CyberArk PAM, CyberArk Defender, Privileged Access Management, CyberArk
- Proofpoint ITS, Proofpoint Certified Identity Threat Specialist, Proofpoint
- CISSP, Certified Information Systems Security Professional, ISC2
- ISSAP, Information Systems Security Architecture Professional, ISC2
- CISM, Certified Information Security Manager, ISACA
- CISA, Certified Information Systems Auditor, ISACA
- CCSP, Certified Cloud Security Professional, ISC2
- ISO 27001 LA, ISO/IEC 27001 Lead Auditor, PECB
- ISO 27001 LI, ISO/IEC 27001 Lead Implementer, PECB
- CIPP/E, Certified Information Privacy Professional/Europe, IAPP
- AWS Security, AWS Certified Security, Specialty, Amazon Web Services
- AWS Architect, AWS Certified Solutions Architect, Associate, Amazon Web Services
- CKA, Certified Kubernetes Administrator, The Linux Foundation
- PRINCE2, PRINCE2 Practitioner, PeopleCert
- HERMES, HERMES Foundation, the Swiss federal project management method, Swiss Confederation
- FCP Cloud, Fortinet Certified Professional, Cloud Security, Fortinet
- Netskope, Netskope Security Cloud Operation & Administration, Netskope
- GitLab CI/CD, GitLab Certified CI/CD Associate, GitLab
- ITIL, ITIL Foundation, PeopleCert
- Six Sigma, Six Sigma Green Belt, Six Sigma
The vision of Marc, Head of the Governance, Risk & Compliance practice.
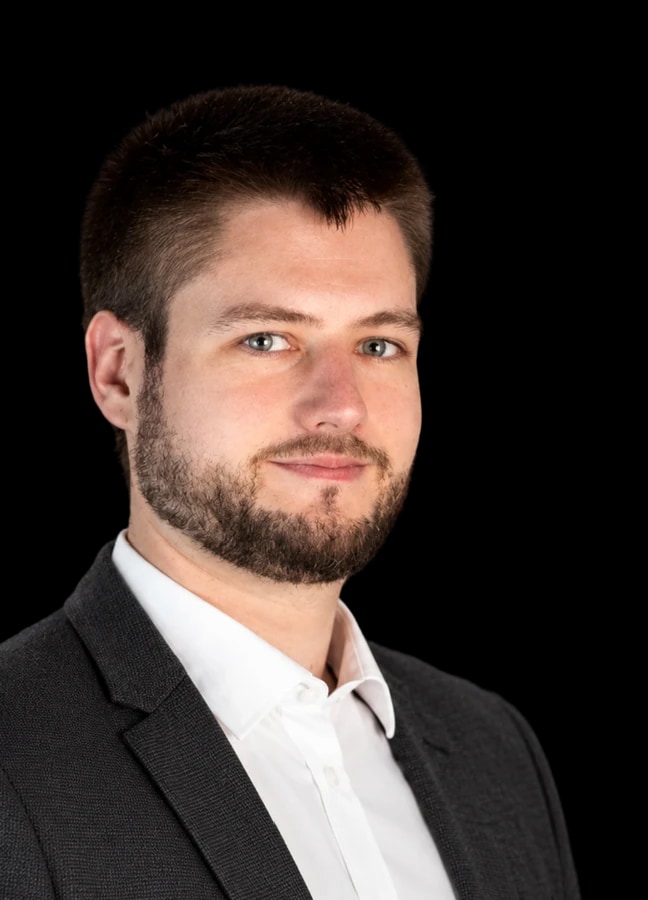
We combine cross-sector expertise, proven methods and innovation to inform your decisions, strengthen your resilience and build lasting trust.
Our training: build your skills in governance, risk and compliance
Explore our courses on business continuity and on building security into your projects.
Ready to structure your cyber governance?
Contact our GRC experts for an initial conversation, with no commitment. We will analyse your context and define the approach best suited to your challenges.
First conversation free and with no commitment. Reply within 48 hours.