CTRL+HACK+ESC, cyber escape game
Take on the role of a hacker, discover the human errors attackers exploit and learn how to prevent them, in an immersive experience played as a team.
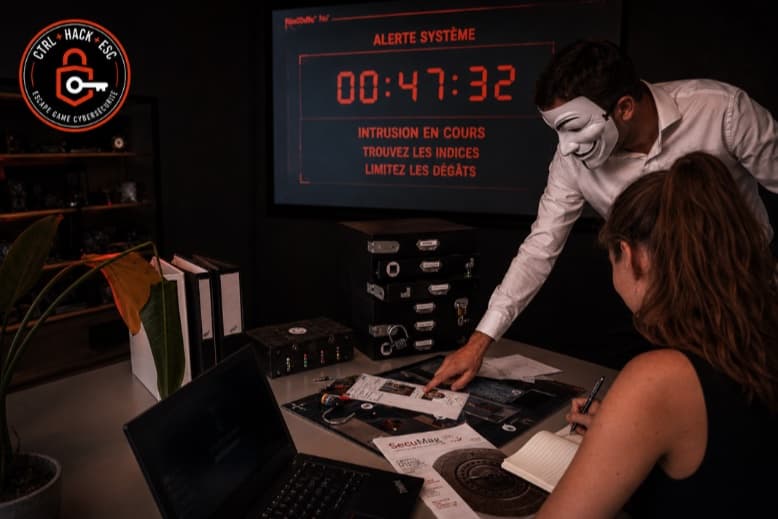
- 60 minutes of immersive play
60 minutes
- per group
- 3 to 6 players
- equipment provided by SecuLabs
- On your premises
- per day
- Up to 50 participants
Infiltrate a fictitious company by exploiting its security flaws
Each team plays the hackers and discovers, through play, how simple actions can change an organisation's level of security.
- Objective
- Get into the server room
- Route
- 6 environments to progress through
- Search
- 2 physical areas with clues and objects
- Approach
- Learning through experience and immersion
Awareness becomes a mission you live through
Classic training is often seen as too theoretical and not very engaging. Turn cyber awareness into an immersive, memorable experience.
In CTRL+HACK+ESC, participants become hackers for a day. They exploit security flaws arising from weak passwords, unlocked computers, phishing and infected USB sticks, among others.
By experiencing cybercriminals' tactics from the inside, participants build reflexes that stick better than after a classic awareness session.
90%
of successful cyberattacks are due to human error.
Briefing, immersion and a teaching debrief
The full session lasts an hour and a half. A SecuLabs cybersecurity expert runs the game.
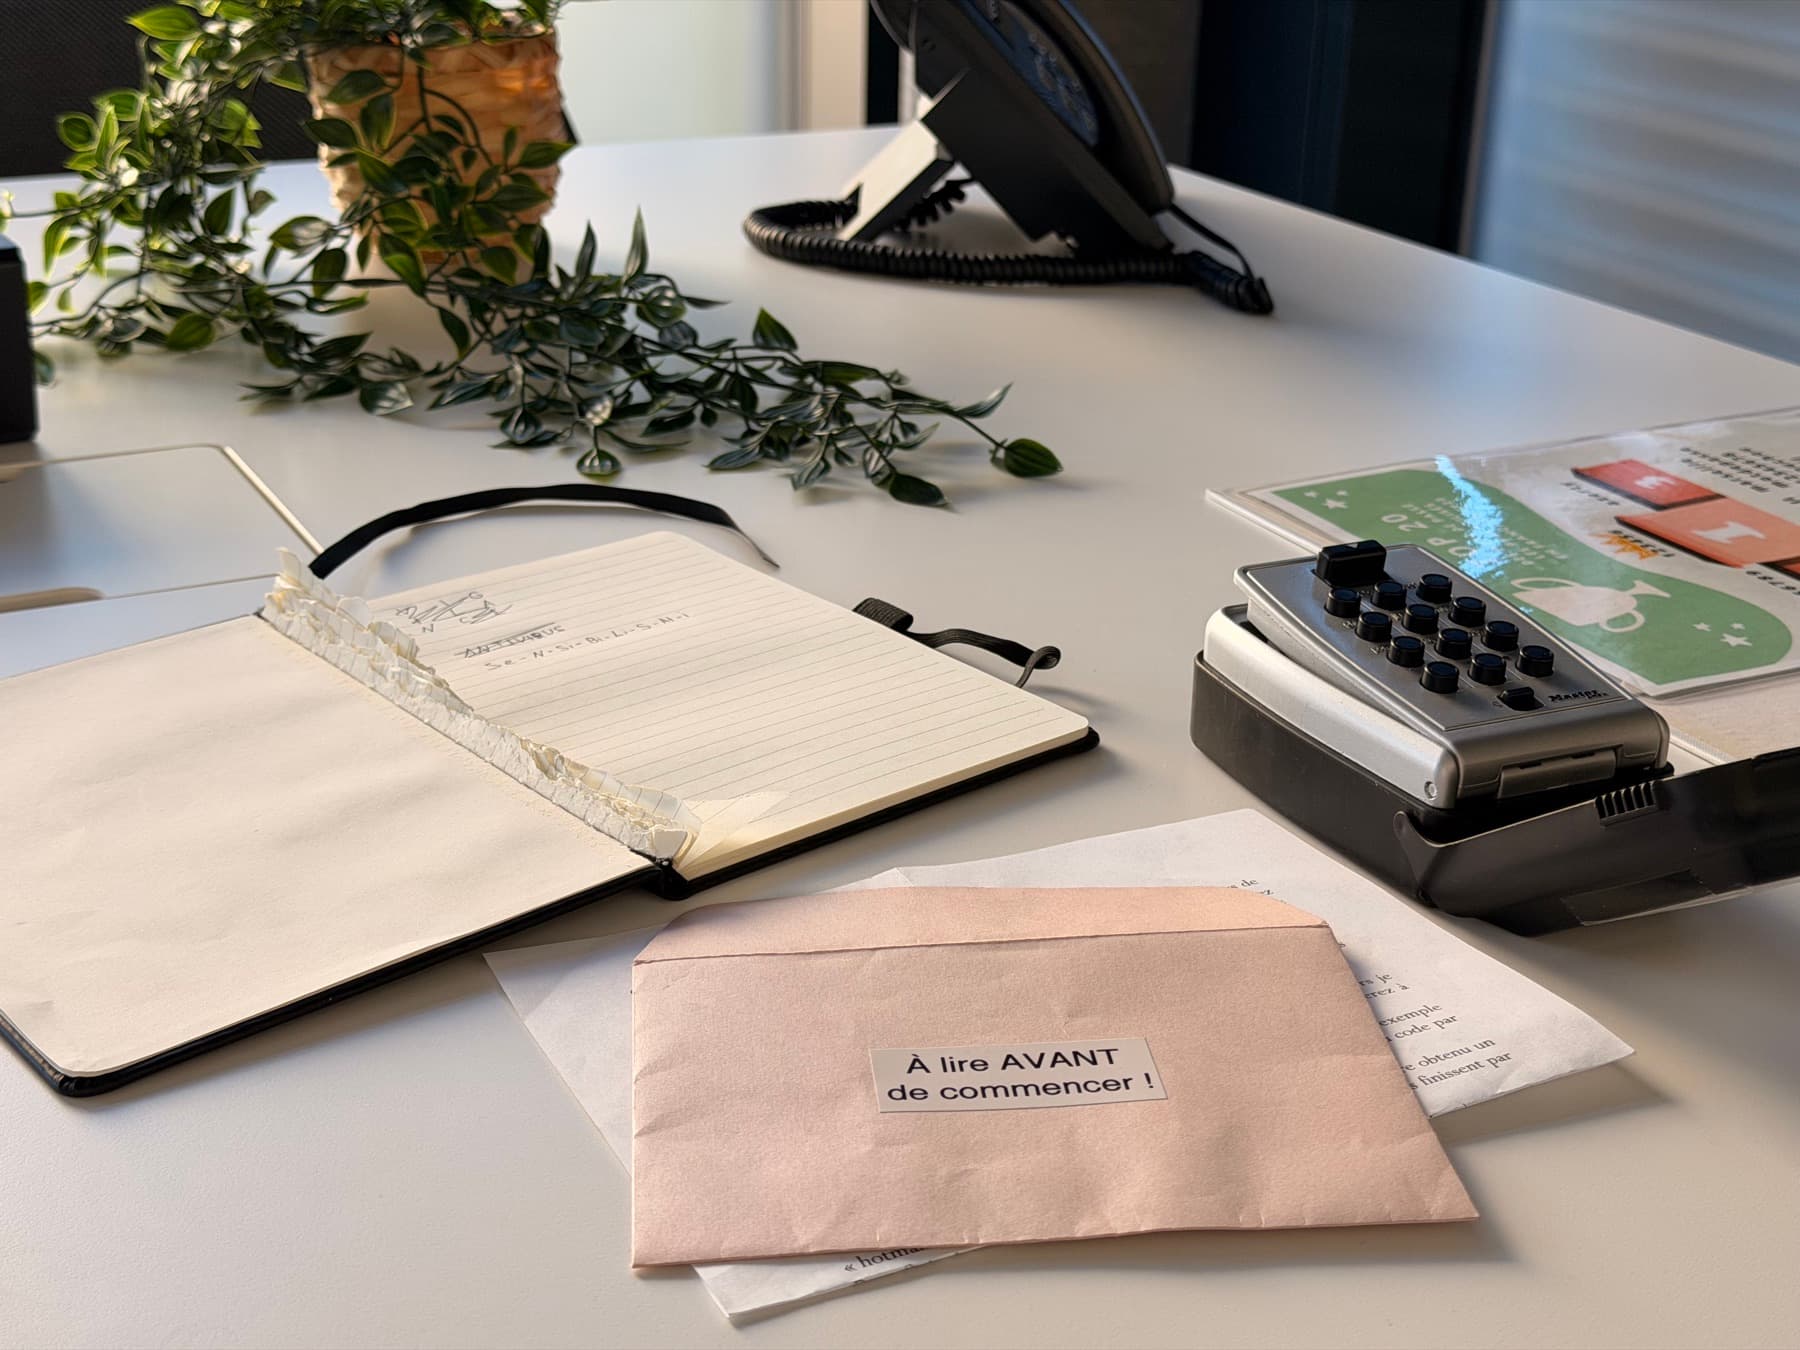
Step 1 · Briefing
Discover the scenario
Participants learn about the mission, the rules of play and the objectives before the game starts.
Step 2 · Game
Make your way through the company
Teams have 60 minutes to get through the rooms, search for clues and exploit the flaws they find.
Step 3 · Debriefing
Link the game to real risks
The facilitator goes back over the mistakes, gauges what the group has learnt and identifies the points that need more attention.
Clues, objects and flaws to exploit
Participants explore 2 physical search areas, examine hidden clues, confidential documents and booby-trapped objects, then make their way through the fictitious company by exploiting its security flaws.
As they explore, they face many security issues that help them build lasting reflexes.
- Strong passwords
- Spotting phishing
- Locking workstations
- Document confidentiality
- Securing the workplace
- Booby-trapped objects
- Personal information and privacy
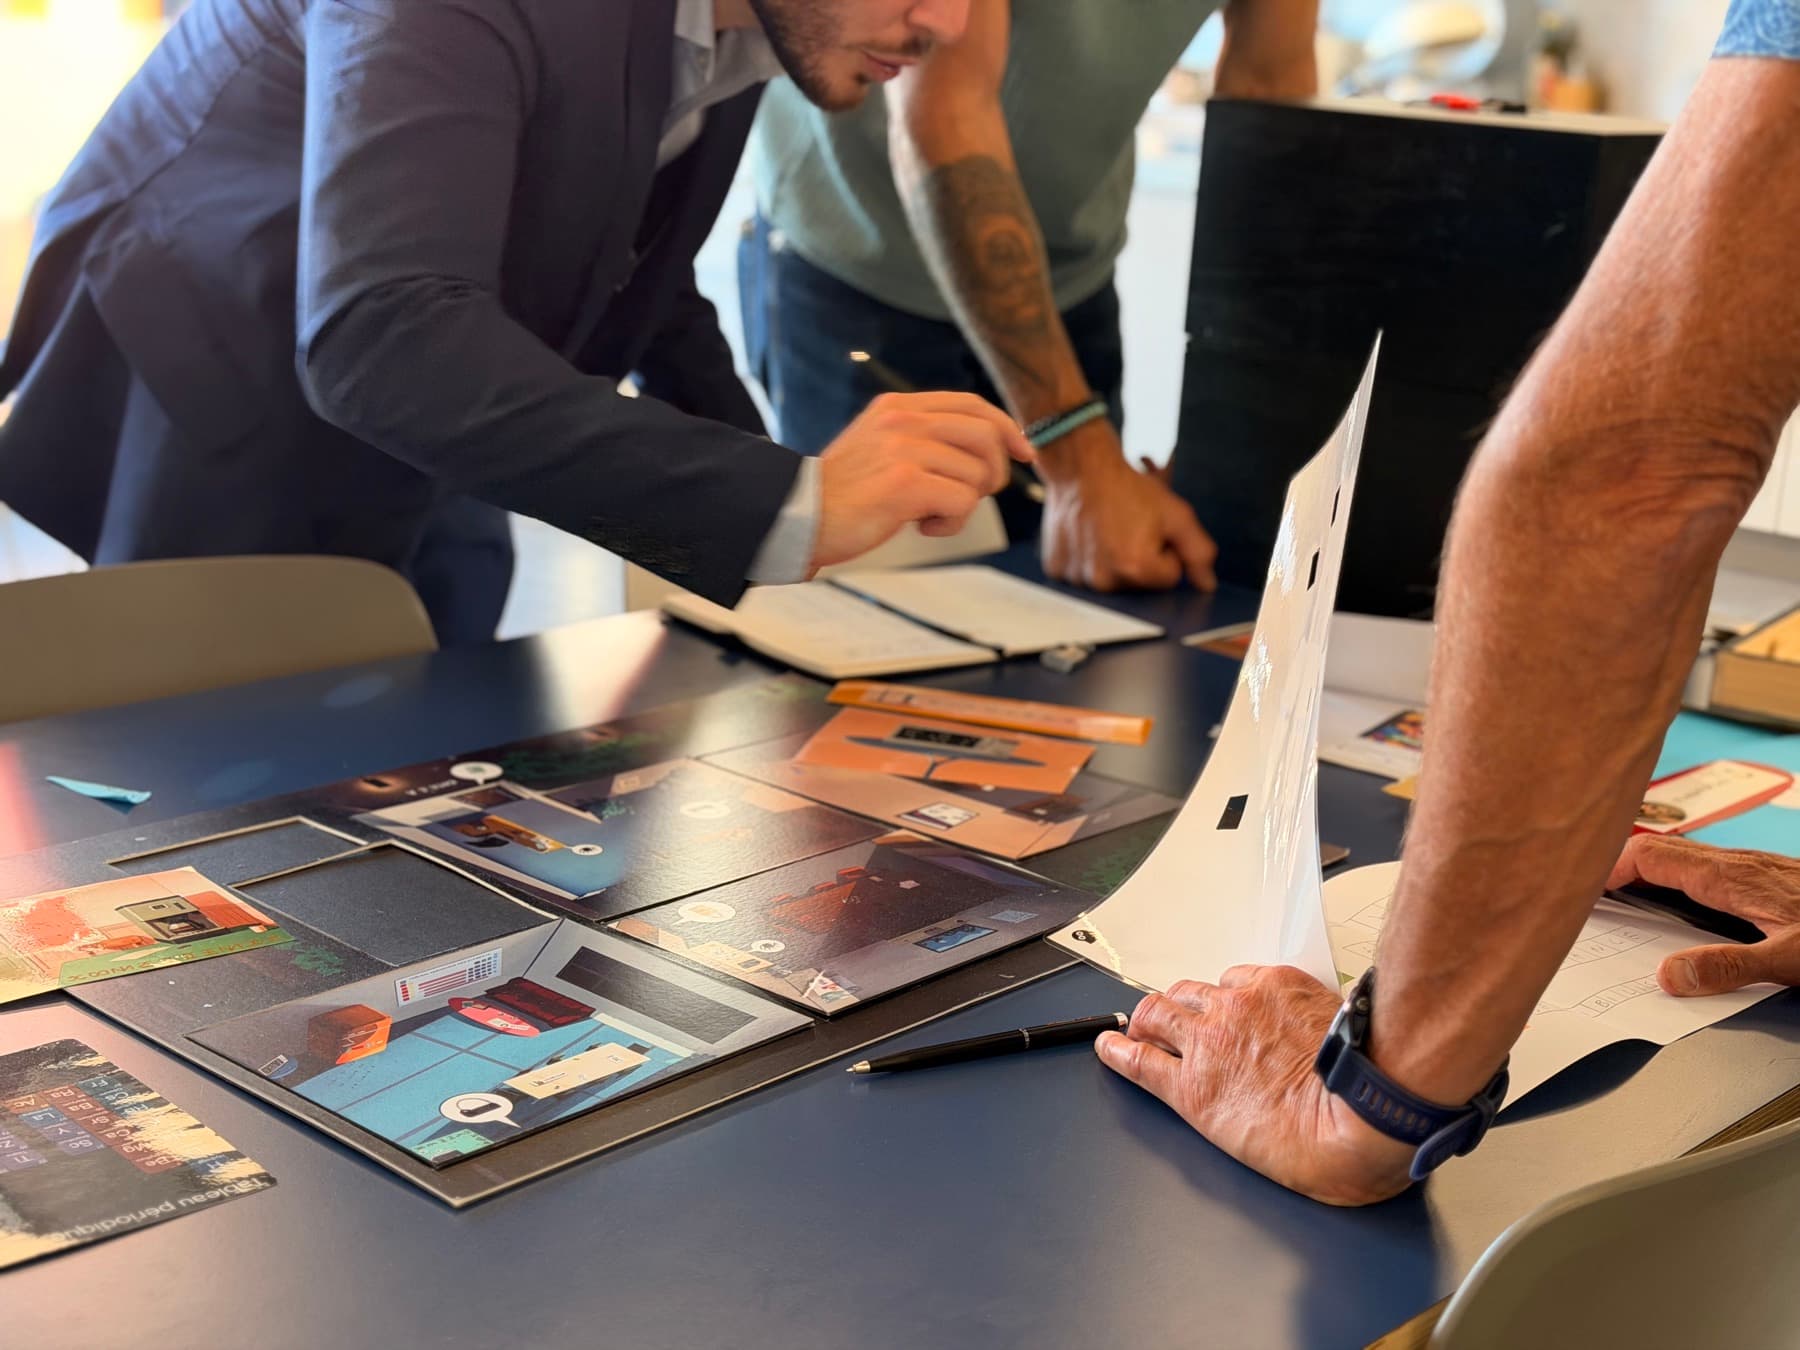
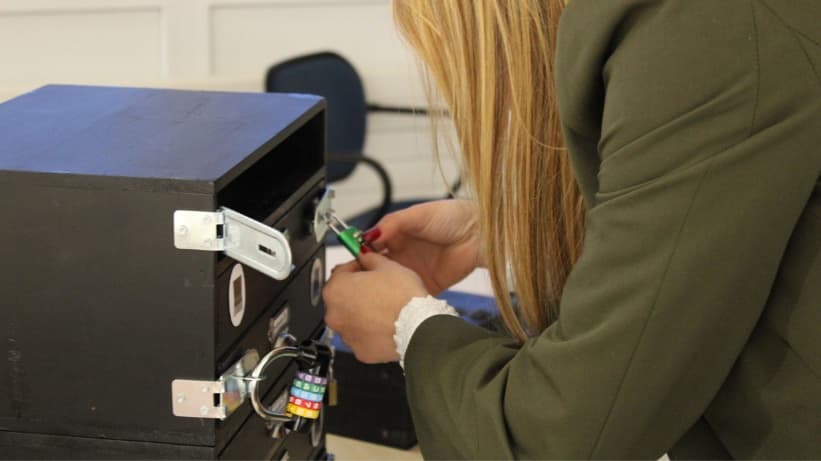
Participants build awareness through practice
Switching perspective puts participants in the attackers' shoes, so they better understand the risks and the consequences of human error.
Understand how cyberattacks exploit human error.
Identify common security flaws in the workplace.
Adopt lasting reflexes: locking workstations, strong passwords and spotting phishing.
Grasp the consequences of a lapse in IT security.
Strengthen team cohesion around a shared cybersecurity culture.
An experience open to every profile
The game can be held on your premises or at SecuLabs.
- Duration
- 90 minutes per sessionBriefing, game and debriefing.
- Teams
- 3 to 6 playersPer group.
- Capacity
- 2 groups in parallelUp to 8 sessions per day.
- Audience
- IT and non-IT profilesNo technical prerequisites.
SecuLabs provides
- All the escape game equipment: the board, the clues, the objects and the search areas.
- A certified cybersecurity expert running the game throughout the session.
- A good practice sheet, given to each participant after the session.
- A certificate of attendance, issued at the end of the session.
What you provide on your premises
- A room available to host the game.
- One main table.
- Two secondary tables.
- A few chairs for the participants.
Book a cyber escape game session
Immersive, playful and hands-on awareness, open to IT and non-IT staff.